Mouad Abid
Mouad Abid — software security engineer. Career rendered as git log --graph --all: every job, degree and training as a branch.
I'm a software security engineer who designs systems where security, performance and weird edge cases collide. I build secure infrastructure, research how systems fail, and occasionally turn those failures into tools, papers and talks.
Currently: now · engineer @ Schwarz Digits. Based in: Heilbronn, DE.
Pages
- Projects: Tools and infrastructure I have built, from detection engineering and cloud security to CTF platforms and red-team automation.
- Timeline: The full graph: work, education, trainings, startups and speaking. Follow each branch from its first commit to where it merges, or filter by track.
- Writing: Notes from taking systems apart: low-level programming, reverse engineering, exploitation and cloud security. Every post, newest first.
- Research: Papers on how systems fail and how to reason about their security, covering attack planning, anti-debugging and cryptographic randomness.
- WhoAmI: My philosophy, the things I value, und co.
- Contact: Code, writing, research and ways to get in touch. These are the remotes where you can find more of my work.
Posts
- Surrounded by Slops: Cloud Red Teaming: On AI slop, Cloud IAM, OPSEC, attack graphs, and why knowing the command is not the same as knowing what the fuck you’re doing.
- PE Hell: A walk through the Windows PE file format — headers, sections, imports — and why parsing it by hand is the first step in malware analysis.
- Do you speak ELF?: The ELF binary format from the inside: headers, sections vs segments, and how the Linux kernel loads your program.
- AWSome Security (Shhhhhh !!) (Part 1): AWS pentesting from an attacker's seat — IAM, credentials, enumeration, and the misconfigurations that hand you the cloud.
- Heap, The Witchcraft Dungeon: How the glibc heap really works — chunks, bins, malloc/free — and how that turns into heap exploitation in CTFs.
- Reverse everything except Love: A fairy-tale style intro to reverse engineering: from source to assembly and back, with the tools that make it click.
- Pointers need painters: Pointers in C explained with pictures — addresses, dereferencing, arrays, and the mistakes that bite beginners.
- Did someone say Memory?: The memory layout of a C program: stack, heap, data, text — and what actually happens when you allocate.
- Makefile or make me a file: Makefiles from zero: rules, variables, pattern rules, and the tricks that make them useful beyond compiling C.
- C from another perspective: How I actually write C — the conventions, habits, and safety rules that keep the code readable and sane.
Research
- Recon as a First-Class Planning Action under Partial Observability: Attack-path planners almost all assume they already know the network. Modelling reconnaissance as a planning action with its own OPSEC cost and information gain reaches the goal in 80.3% of randomised Active Directory graphs against 52.3% for a two-phase baseline — but only once the pursuit is directed and multi-step.
- HOP: Hook Oriented Programming: Licence checks fall to debuggers, and anti-debugging in turn falls to whatever an attacker can patch out. HOP is a Linux anti-debugging design that claims the one debugger slot a process is allowed to have, so the protection has to be evicted before a debugger can attach at all.
- RCPRNG: Robust Complete PRNG: Cryptographic PRNG models assume unlimited compute and clean entropy; embedded systems have neither, and there entropy accumulation and generation share the same scarce resources. RCPRNG folds both into one security model whose completeness property carries guarantees across arbitrary state transitions, and shows the Gaži-Tessaro sponge construction satisfies it.
Projects
- Decnique: Designed and built a formal language and evaluation framework for measuring SIEM detection coverage against adversarial techniques over a common event model using nothing but pure math.
- IAMouflage: Designed and built a detection-to-technique visualization using Neo4j, mapping methodName (detection) to permission (technique) for better visibility during red teaming.
- Verisentinel: Experimental GCP IAM decision-support tool that checks language-model proposals against permission feasibility and modeled detection coverage before presenting actions for human approval.
- mals3scan: Serverless AWS security pipeline that scans every file uploaded to S3 with YARA rules for malware and sensitive data, firing real-time alerts for incident response.
- GCPdvi: Deliberately vulnerable GCP IAM training lab defined in Terraform, with five identities linked by progressively harder, keyless privilege-escalation paths.
- L3AK CTF 2025 Infra: Designed and built the infrastructure hosting the L3AK CTF 2025 event on GCP, handling more than 10k concurrent users and millions of requests.
- redteam-copilot: A GCP IAM red-teaming harness, with a deterministic propose-then-verify architecture.
- anti-debug: Experimental Linux anti-debugging research using ptrace, a modified libc, and syscall remapping to explore hook-oriented programming.
- CoGraph: Red-team knowledge graph prototype combining structured security datasets with an LLM extraction pipeline and graph-based retrieval.
- AI-Dilemma: Research on AI red and blue teaming, with a Typst paper and a notebook prototype for classifying prompt intent and selecting security policy actions.
- ft_containers: Reimplemented C++ STL vector and map containers, including iterators, allocator handling, and a red-black tree, with comparison tests against the standard library.
- readelf: ELF inspection tool written in C, with separate parsers for 32-bit and 64-bit binaries and their headers.
- ft_minishell: Designed and built my own shell in pure C.
- ft_IRC: Designed and built an IRC server in pure C++.
- libasm: Recreated basic libc functions in x86-64 assembly, including string operations, memory duplication, and read/write wrappers.
- philo: Dining philosophers simulation in C using threads and mutexes to coordinate shared forks, meal timing, and termination.
- cyberdayCTF: Public Cybersecurity Day CTF challenges, solutions, and container launch scripts spanning web, cryptography, forensics, pwn, reversing, and geolocation.
- L3AK CTF 2024 Infra: Developed the infrastructure hosting the L3AK CTF 2024 event, handling more than 1k concurrent users with zero downtime.
- Landing Graph: Designed and built my own personal blog based on "git log --graph --all".
- bounties: Hackathon prototype for verifying bug bounty award emails with vlayer and recording on-chain badges and researcher reputation.
Languages I speak
- Arabic: native
- English: C1
- German: C1
- French: C1
Profiles
Projects
Tools and infrastructure I have built, from detection engineering and cloud security to CTF platforms and red-team automation.
Decnique
- pinned: true
- visibility: Public
- start: 2026-08
- end: now
- domains: cloud-security
- languages: python
- topics: detection-engineering, formal-methods
- updated: 2026-10-01
- link: https://github.com/moabid42/decnique
Designed and built a formal language and evaluation framework for measuring SIEM detection coverage against adversarial techniques over a common event model using nothing but pure math.
IAMouflage
- start: 2026-05
- end: 2026-08
- domains: cloud-security, offensive-security
- languages: go
- topics: iam, detection-engineering, attack-modeling
- updated: 2026-08-27
- link: https://github.com/moabid42/IAMouflage
Designed and built a detection-to-technique visualization using Neo4j, mapping methodName (detection) to permission (technique) for better visibility during red teaming.
Verisentinel
- domains: cloud-security, offensive-security
- languages: python
- topics: iam, attack-planning, privilege-escalation, formal-methods, language-models
- updated: 2026-09-03
- link: https://github.com/moabid42/Verisentinel
Experimental GCP IAM decision-support tool that checks language-model proposals against permission feasibility and modeled detection coverage before presenting actions for human approval.
mals3scan
- pinned: true
- visibility: Public
- domains: cloud-security
- languages: python
- topics: detection-engineering, malware-detection
- updated: 2026-09-03
- link: https://github.com/moabid42/mals3scan
Serverless AWS security pipeline that scans every file uploaded to S3 with YARA rules for malware and sensitive data, firing real-time alerts for incident response.
GCPdvi
- domains: cloud-security, offensive-security
- topics: iam, privilege-escalation
- updated: 2026-07-18
- link: https://github.com/moabid42/GCPdvi
Deliberately vulnerable GCP IAM training lab defined in Terraform, with five identities linked by progressively harder, keyless privilege-escalation paths.
L3AK CTF 2025 Infra
- pinned: true
- visibility: Internal
- org: L3AK TEAM
- start: 2025-04
- end: 2025-07
- domains: infrastructure
- topics: distributed-systems, high-availability, caching
Designed and built the infrastructure hosting the L3AK CTF 2025 event on GCP, handling more than 10k concurrent users and millions of requests.
redteam-copilot
- pinned: true
- visibility: Internal
- domains: cloud-security, offensive-security
- topics: iam, attack-planning, language-models
A GCP IAM red-teaming harness, with a deterministic propose-then-verify architecture.
anti-debug
- domains: offensive-security, systems-programming
- languages: c, assembly
- topics: anti-debugging, reverse-engineering
- updated: 2024-03-12
- link: https://github.com/moabid42/anti-debug
Experimental Linux anti-debugging research using ptrace, a modified libc, and syscall remapping to explore hook-oriented programming.
CoGraph
- domains: offensive-security
- languages: python
- topics: knowledge-graphs, attack-modeling, language-models
- updated: 2026-04-20
- link: https://github.com/moabid42/CoGraph
Red-team knowledge graph prototype combining structured security datasets with an LLM extraction pipeline and graph-based retrieval.
AI-Dilemma
- domains: ai-security
- languages: python
- topics: red-teaming, threat-modeling, prompt-injection, language-models
- updated: 2026-03-11
- link: https://github.com/moabid42/AI-Dilemma
Research on AI red and blue teaming, with a Typst paper and a notebook prototype for classifying prompt intent and selecting security policy actions.
ft_containers
- org: 42 Heilbronn
- domains: systems-programming
- languages: cpp
- topics: data-structures, memory-management
- updated: 2023-01-27
- link: https://github.com/moabid42/ft_containers
Reimplemented C++ STL vector and map containers, including iterators, allocator handling, and a red-black tree, with comparison tests against the standard library.
readelf
- domains: systems-programming, offensive-security
- languages: c
- topics: binary-formats, reverse-engineering
- updated: 2023-10-10
- link: https://github.com/moabid42/readelf
ELF inspection tool written in C, with separate parsers for 32-bit and 64-bit binaries and their headers.
ft_minishell
- org: 42 Heilbronn
- start: 2022-06
- end: 2022-09
- domains: systems-programming
- languages: c
- topics: parsing, concurrency
- updated: 2023-10-10
- link: https://github.com/moabid42/shell
Designed and built my own shell in pure C.
ft_IRC
- org: 42 Heilbronn
- start: 2022-10
- end: 2022-11
- domains: systems-programming
- languages: cpp
- topics: networking, concurrency
- updated: 2023-05-02
- link: https://github.com/moabid42/mini_IRC
Designed and built an IRC server in pure C++.
libasm
- org: 42 Heilbronn
- domains: systems-programming
- languages: assembly
- topics: memory-management, system-calls
- updated: 2023-10-10
- link: https://github.com/moabid42/libasm
Recreated basic libc functions in x86-64 assembly, including string operations, memory duplication, and read/write wrappers.
philo
- org: 42 Heilbronn
- domains: systems-programming
- languages: c
- topics: concurrency
- updated: 2022-08-08
- link: https://github.com/moabid42/philo
Dining philosophers simulation in C using threads and mutexes to coordinate shared forks, meal timing, and termination.
cyberdayCTF
- org: 42 Heilbronn
- domains: offensive-security, application-security
- languages: python
- topics: security-education, binary-exploitation
- updated: 2025-03-04
- link: https://github.com/moabid42/cyberdayCTF
Public Cybersecurity Day CTF challenges, solutions, and container launch scripts spanning web, cryptography, forensics, pwn, reversing, and geolocation.
L3AK CTF 2024 Infra
- org: L3AK TEAM
- start: 2024-04
- end: 2024-05
- domains: infrastructure
- topics: distributed-systems, high-availability, caching
Developed the infrastructure hosting the L3AK CTF 2024 event, handling more than 1k concurrent users with zero downtime.
Landing Graph
- start: 2026-09
- end: now
- domains: web-development
- languages: javascript
- topics: content-publishing
- updated: 2026-10-12
- link: https://github.com/moabid42/landing-graph
Designed and built my own personal blog based on "git log --graph --all".
bounties
- org: ETHGlobal Prague
- domains: application-security
- languages: solidity
- topics: cryptographic-proofs
- updated: 2025-06-01
- link: https://github.com/moabid42/bounties
Hackathon prototype for verifying bug bounty award emails with vlayer and recording on-chain badges and researcher reputation.
WhoAmI
My philosophy, the things I value, und co.
Usually, when I write something this long, it is because I noticed something cursed and I need to tell someone about it.
This time, the question is a little closer to home.
So, Who am I, once you get past the job title?
Apparently my own documentation could use some work too :)
So, here is some of it. The things that shaped me, the things I keep coming back to, and the questions I am still working on.
Before the terminal, there was an AC unit
I started working at thirteen, right after finishing primary school. I spent my summers going around the city, fixing heaters and installing ACs.
And honestly, you learn quite a bit about people when you work in their homes.
Some respected the work and appreciated that you knew how to fix their problem. Others treated you like they are doing you a FAVOR by calling YOU for help.
Like dude you called me for help. HELLO???
Then there were the ones who wanted the whole job done, cleaned and sometimes with an additional "can you check my refrigerator" task but somehow find it suddenly very inconvinient and expensive to pay for the agreed installation.
This was my first interaction with NPCs fr :\
You quickly learn that doing the job and dealing with the client are two separate skills. I had to learn both. And along the way, I started understanding what it actually takes to earn money, and thus value money.
Don't get the wrong idea tho.
My family always made sure I had a warm meal, clothes, and everything I "needed".
It is true we never had the luxuary to get every fish in the ocean. BUT! My father made sure we learned how to fish ourselves.
Toys. My first phone. My first laptop. My first PC. Trips. Going outs.
Summer jobs, errands, good grades. That was how I earned them.
And I'm glad he raised me that way. I learned to manage my money, take responsibility for myself, and appreciate the effort behind what I owned. It's hard to take something for granted when you remember the work that paid for it.
So yes, I am still proud that I can install an AC.
AH! And whenever I go back to Morocco, I still go out on jobs with my uncle. It brings back a lot of memories, and I get to spend that time with him.
Life wasn't as pink as I am trying to paint it. But you know what they say.
Don't let a few bad apples spoil the whole bunch.
Eren and Torfin showed me that Freedom can be either "Destructive & External" or "Constructive & Internal"
Germany Arc
I came to Germany on my own at nineteen.
That sentence is easy to put on a timeline. The parts underneath it take a little more space.
There were nights sleeping on the street. Nights sleeping at school. Surviving on whatever was available. Working more than three hundred hours a month and continuing to support myself without turning back to ask for money or help.
Those are parts of my story too.
It was indeed God's plans. And only when you zoom out, you see how all the pieces fit together.
When I look back, I see how much my childhood had prepared me for what came next. I had already learned to work, to adapt, to deal with difficult situations, and all only with what I had available.
Without that upbringing, I honestly think I would have given up in my first month.
That is probably why I trust my ability to adapt so much. I learn quickly, and I can find my footing in a new environment. I have had to do it often enough that it became second nature.
What matters to me is being able to change with the situation while keeping hold of who I am.
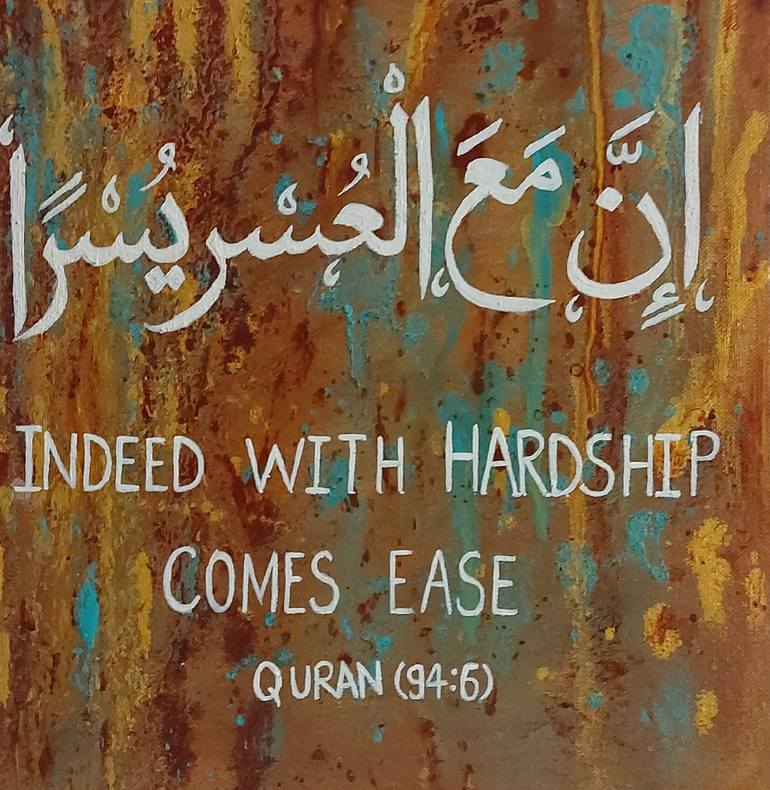
"sabr" is the only word without an opposite
Curiosity built this mind
Almost everything I know started with a question.
Why does this work? What happens if it breaks? Why do people behave that way? What am I missing?
Sometimes that question leads to a tool. Sometimes to a paper or a piece of writing. Sometimes it just leaves me with a much better question and considerably more tabs open than I planned.
An extremely efficient lifestyle, as you can imagine.
But I like it. I like learning something well enough that I can explain it, challenge it, or build with it. I like the moment when something that looked completely unfamiliar begins to make sense.
That curiosity reaches well beyond my work. I read and write about life and death, AI, human behaviour, faith, and the things I do not think science has fully explained. A question does not have to become useful at work for me to want to spend time with it.
Writing is how I work through a lot of these thoughts. Putting something into words makes me sit with it a little longer. It gives me a chance to see what I actually mean, and where I still have questions.
So yes, curiosity built this mind.
And, I would like to keep giving it room to do that.
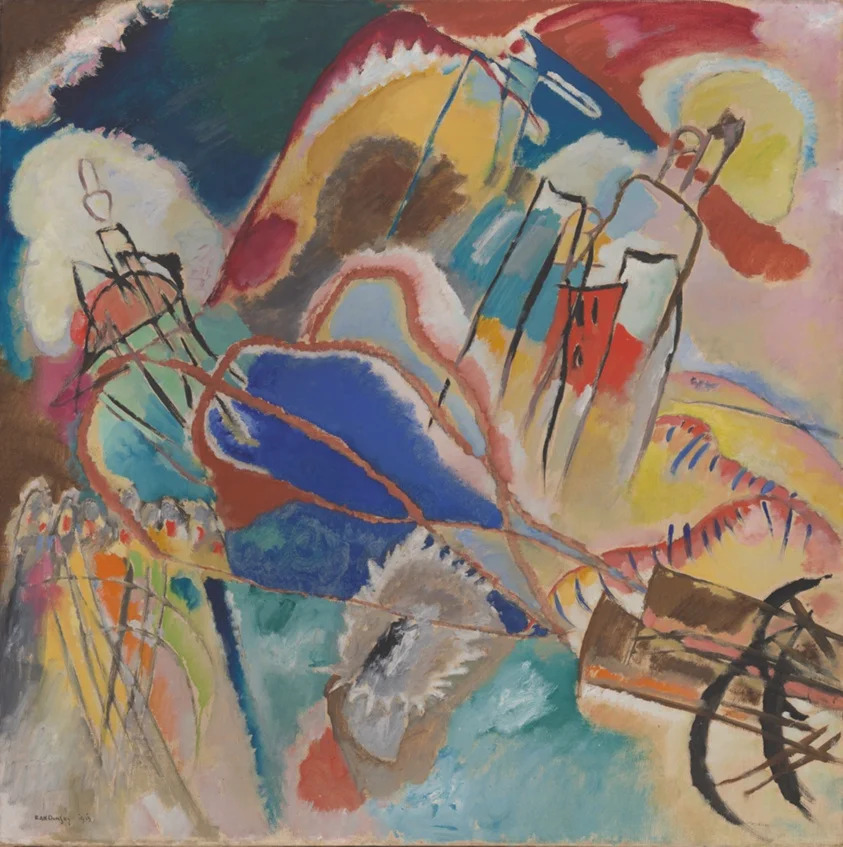
Vasily Kandinsky, Improvisation No. 30 (Cannons), 1913. Image courtesy of the Art Institute of Chicago
Beginner. Again.
I have never been particularly afraid of starting from zero.
A new field, a new environment, a new sport. There is always something I do not know yet, and I am happy to be the person learning it.
That has been true throughout my life. I have a black belt in taekwondo. I spent a couple of years kickboxing and tried judo for a while. Then I started calisthenics, and more recently, bouldering.
Turns out knowing one sport does not automatically make gravity more cooperative in the next one.
Good to know :)
I enjoy being a beginner because there is so much to discover. You pay attention. You try things. You make mistakes that someone more experienced can see coming from across the room. Then, slowly, you improve.
I want to keep doing that in as many parts of my life as I can. Learning, changing, trying again. To me, that is a large part of what being alive is for.
And football has been there for as long as I can remember. I still play with friends every week. After all those new beginnings, it is good to have something I keep coming back to as well.
This guy is THE representation of Beginner and Again
Sweat is the prize
There is a line I keep coming back to:
When the trophy can be bought, sweat is the new prize.
I care about the effort that makes an achievement mean something to me. I want to know what it took, what I learned along the way, and what I can actually do when it is over.
That feeling has followed me from summer work to sport to the work I do now. Earning my first laptop meant something because I knew what had gone into it. Learning a skill means something because I remember being unable to do it.
The difficult part gives the result weight.
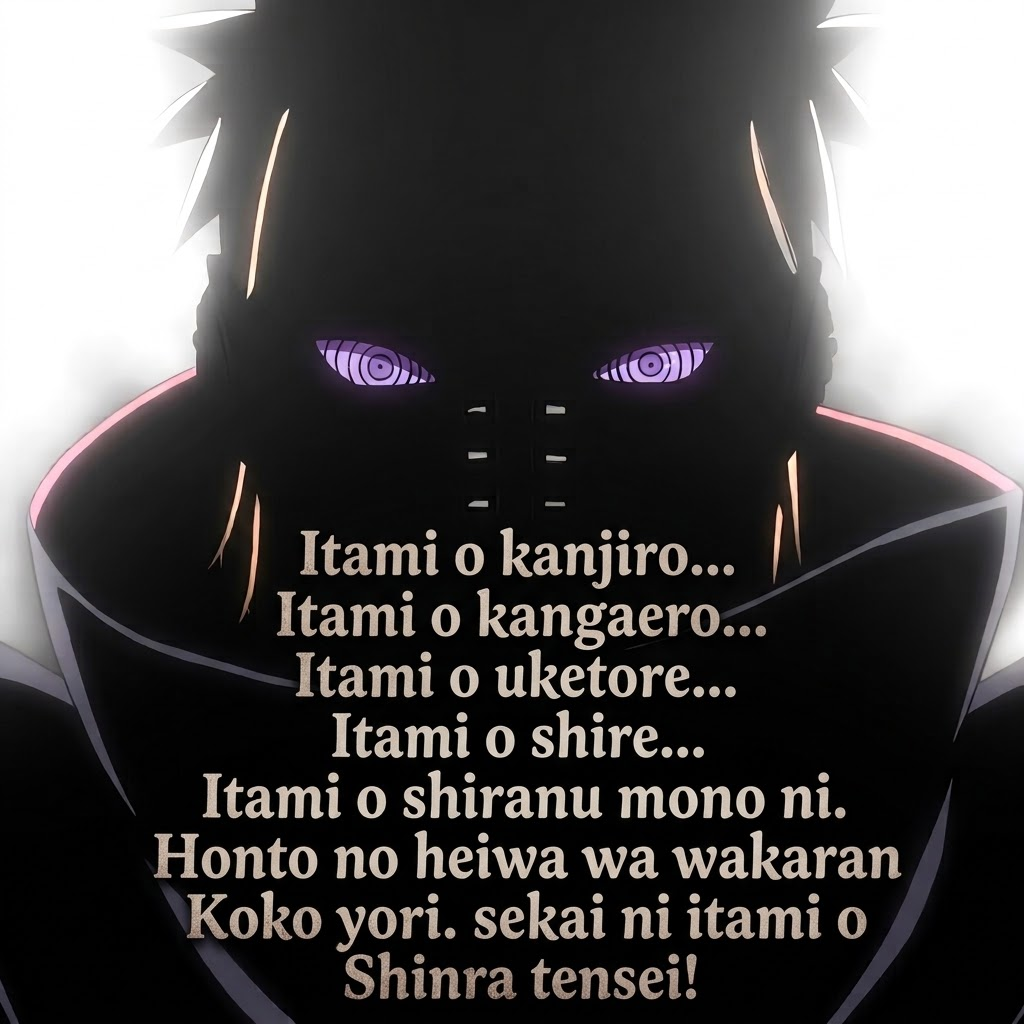
And yes, some of the words that have stayed with me come from Naruto. Pain's insistence on knowing pain before understanding peace speaks to something I recognise in my own life.
Struggle changes how I experience happiness. Effort changes how I experience achievement. After being through something difficult, I understand the relief on the other side differently.
That has shaped me. It has also made the good parts of life feel much less ordinary.
Life is the currency
“The cost of a thing is the amount of what I will call life which is required to be exchanged for it…”
Henry David Thoreau, Walden, “Economy”
I think about that a lot.
I know how to work hard. I am still learning how to decide what deserves that work.
Something can cost money, but it can also cost evenings, attention, energy, and time with people I care about. Looking at the price in terms of my own life makes me pay attention to what I am choosing.
I want to spend it on things that matter to me. Learning. Work I care about. Family. Experiences I want to have. I also want to notice when I am giving too much of it to something that does not deserve it.
I love the field I work in. My work and my hobbies have always overlapped, and I am grateful for that. Having something I want to wake up and work on gives me a reason to look forward to the next challenge.
There are other things I want to make room for too.
I think it is "AboutTime" you watch this masterpiece if you haven't
The things I come back to
Family matters to me more than I can easily explain.
Ask me how a system works and I can probably talk for hours. Ask me why family matters so much, and the answer gets harder to put into words. I just know that it sits close to the centre of what I want from life.
Maybe that is why I keep coming back to the memories in this page. My father's way of raising me. Going out with my uncle when I am back in Morocco. The things I learned early that followed me into a completely different life.
I want to keep growing without losing those parts of myself.
There is another line I love:
“But how could you live and have no story to tell?”
Fyodor Dostoevsky, White Nights
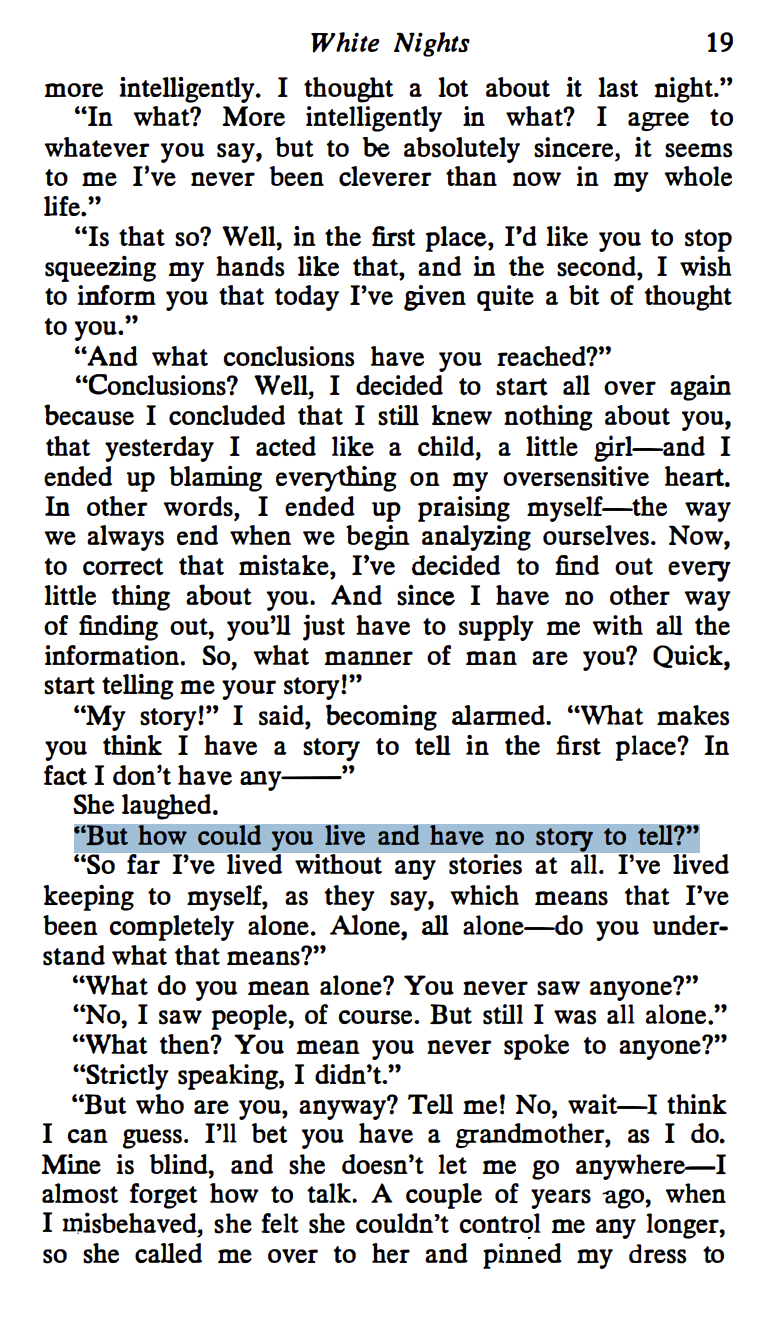
I want a story I have taken part in writing. One where I asked the questions, made the choices, and was willing to begin again when I needed to.
I am still figuring out what that looks like. I expect some of what I write here to change as I live more, learn more, and understand things differently.
That feels right to me.
I think we create ourselves through the things we keep choosing to do. Every new beginning gives me another chance to work on the person I am becoming.
So, that is where I am for now.
Still curious. Still learning. Still playing football on Mondays.
Let's see what the next chapter looks like :)
Career
work
Private Tutor, freelance
- org: Morocco
- start: 2020-08
- end: 2022-01
- topics: math, english, french
- time: part-time
- description: Tutored 10+ students (ages 4–18) in math, physics and English. Grounded each concept in its history and reasoning, prioritizing understanding over memorization and achieving a minimum 40% improvement in grades.
Cloud Security Engineer, internship
- org: Haufe Group · Freiburg
- start: 2023-03
- end: 2023-08
- topics: aws, lambda, terraform
- time: full-time
- link: https://www.haufegroup.com/en
- description: Designed MalS3Scan, a serverless AWS malware-detection pipeline processing ~10k files/day across thousands of buckets, batch-dispatching to parallel Lambda scanners against a centralized YARA rule DB, with automated alerting for incident response.
System Engineer, POS systems
- highlight: true
- org: Schwarz Digits · Weinsberg
- start: 2023-09
- end: 2025-07
- topics: rhel, OS, infra, pentest
- time: full-time
- link: https://schwarz-digits.de/en
- description: Owned integration and security for 150,000+ point-of-sale systems with zero downtime.
Software Security Engineering tutor & speaker
- org: 42 Heilbronn & Arkadia
- start: 2023-11
- end: 2025-11
- topics: teaching, software, security, infrastructure
- time: part-time
- link: https://www.42heilbronn.de/en/
- description: Taught thousands of students live advanced classes on C, data structures, reverse engineering and binary exploitation. Hosted Cybersecurity Day for 100+ people onsite.
Offensive Security Engineer
- highlight: true
- org: Schwarz Digits · Berlin, remote
- start: 2025-07
- end: now
- topics: red team, infra, research
- time: full-time
- link: https://schwarz-digits.de/en
- description:
- Owned and Designed a dynamic zero-trust orchestration platform across STACKIT and GCP, via Kata microVMs and Cilium eBPF host rounting over WG transit mesh.
- Owned and designed a GCP IAM red-teaming harness with a deterministic propose-then-verify architecture.
- Conducted security reviews and code assessments across STACKIT’s global cloud infrastructure and applications serving millions of users.
- Engineered EDR evasion techniques by reverse-engineering Windows kernel telemetry and building custom payload delivery tooling in C and assembly.
Software Security Engineer
- highlight: true
- org: Mingabyte · Munich, remote
- start: 2025-12
- end: now
- topics: rust, threat modeling, TISAX
- time: part-time
- link: https://mingabyte.de/en/
- description:
- Designed a secure high-load AI inference system in Rust and Python.
- Led the execution and delivery of the company's TISAX certification in less than 350 hours.
education
FSTT, MIP
- org: Université Abdelmalek Essaâdi
- start: 2020-09
- end: 2022-02 (dropped)
- topics: math, informatics, physics
- link: https://fstt.uae.ac.ma/
- description: First reality check.
Core curriculum, software engineering
- highlight: true
- org: 42 Heilbronn
- start: 2022-03
- end: 2023-03
- topics: c, c++, systems
- link: https://www.42heilbronn.de/en/
- description: Intensive peer-to-peer program: C, C++, systems programming, networking, full-stack.
B.Sc. Computer Science, dual study
- highlight: true
- org: DHBW Mannheim
- start: 2023-09
- end: 2026-08
- topics: math, software engineering, security, cryptography
- link: https://www.mannheim.dhbw.de/
- description: Software engineering, IT security, network security, cryptography, alongside full-time work, the whole way through.
trainings
COAE (Certified Offensive AI Expert)
- org: HackTheBox
- start: 2026-04
- end: 2026-07
- topics: ai, redteam
startups
Founder & captain, L3AK
- highlight: true
- org: Security research team · 50+ active members
- start: 2023-03
- end: 2025-10
- topics: ctf, red team, community
- link: https://ctftime.org/team/220336
- description: Founded and led a team of 100+ security researchers across 20 countries, achieving a consistent top-10 worldwide CTFtime ranking, with results at DEF CON CTF and Google CTF.
CTO
- org: xTID
- start: 2024-04
- end: 2025-11
- topics: nestjs, nextjs, ipfs, solidity, infra
- time: part-time
- link: https://xtid.io/
- description: Designed and built a secure decentralized document verification system handling 1k+ transactions a month.
CEO
- org: lyraix
- start: 2025-11
- end: 2026-04
- topics: ai-security, harness, fine-tuning, data-pipelines
- time: part-time
- link: https://lyraix.ai/blog/
- description: Founded lyraix, an AI security lab, and designed LyraixGuard, a real-time AI guardrail system with 300+ downloads on Hugging Face.
speaking
HTB International Meetup
- highlight: true
- org: HackTheBox · EliteSec
- date: 2025-06
- topics: reversing, anti-debug, maldev
- link: https://www.linkedin.com/posts/1337-coding-school_hackthebox-elitesec-42network-activity-7335361736692154370-JZ2i?utm_source=share&utm_medium=member_desktop&rcm=ACoAADhzXYcBfwkDrhdnjiwVFhzoKTLSlT3A7D8
- description: Presented my research on advanced Linux anti-debugging mechanisms, titled "Hook Oriented Programming".
NULLHAT Morocco
- org: HackerOne · EliteSec
- date: 2025-10
- topics: reversing, pwn
- link: https://lnkd.in/p/edeUMhFC
- description: Co-organized a HackerOne meetup in Morocco, delivering high-quality challenges and talks.
Cyber Odyssey
- org: 1337 · AkaSec
- date: 2025-12
- topics: crypto, IoT, CSPRNG
- link: https://www.linkedin.com/posts/akasec-1337_meet-our-speakers-first-we-have-mouad-abid-activity-7393334107402838016-SN4D?utm_source=social_share_send&utm_medium=member_desktop_web&rcm=ACoAADhzXYcBfwkDrhdnjiwVFhzoKTLSlT3A7D8
- description: Presented my research on CSPRNG in embedded systems, titled "Robust Complete PRNG".